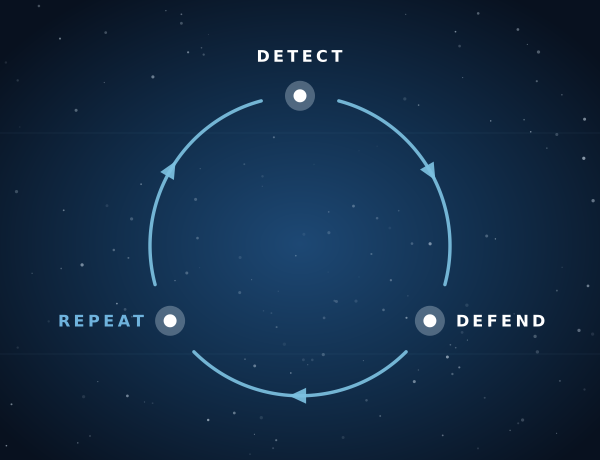
Detect. Defend. Repeat.
Microsoft security expertise, working alongside your team.
Luna Cyber is a New Zealand consultancy specialising in Microsoft security. We find out where you actually stand, do the work to improve it, and stay available as your estate changes. Your team keeps ownership. We bring the depth they do not have in house.
How we work
Three ways to bring us in
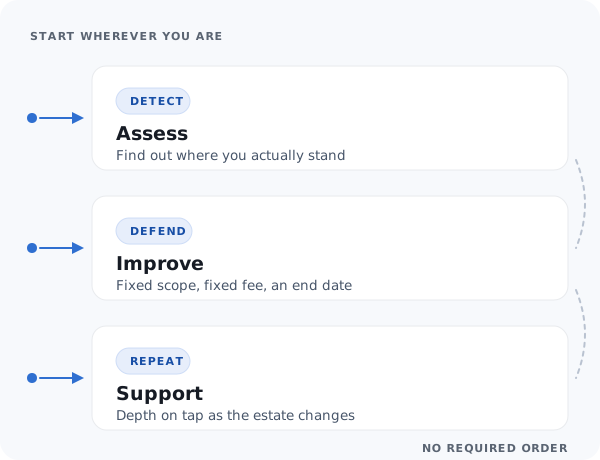
Start wherever you actually need help. There is no compulsory first step, and nothing you have to buy into before we will talk about the problem in front of you.
Assess
Find out where you stand. A scoped review of your tenant, a single product area, a design you are about to build, or the provider you already pay to run your security.
What an assessment covers → DefendImprove
Get the work done. A defined piece of engineering with a fixed scope, a fixed fee and an end date. Hardening, deployments, migrations, or clearing a backlog nobody has had time for.
How projects run → RepeatSupport
Keep the depth on tap. Ongoing capacity for your team, scheduled re-assessment, and engineers who already know how your estate is put together.
What ongoing support looks like →What we cover
The whole Microsoft security stack
Five areas, and the seams between them. Most of the problems worth finding do not sit neatly inside one product, which is why we work across all of it rather than specialising in one.
Identity and access
Entra ID, Conditional Access, privileged access, authentication methods, guest access and app consent. The perimeter that actually matters.
Learn more → DetectionThreat protection and detection
Defender across endpoint, identity and Office 365, and Microsoft Sentinel: coverage, tuning, detection quality and what your ingestion is costing you.
Learn more → DataData protection and endpoint
Purview labels, DLP and retention, plus Intune, device compliance and endpoint hardening. Protecting the data itself, and the devices it lands on.
Learn more → CloudAzure and cloud posture
Defender for Cloud, Azure Policy, RBAC and subscription design, and the exposure that comes with infrastructure nobody has reviewed in a while.
Learn more → CopilotCopilot and AI readiness
Copilot does not create oversharing. It surfaces the oversharing you already had, instantly and to everyone who asks. Readiness, governance and agent identity.
Learn more →Working together
A partner, not a supplier.
We are not interested in being the consultancy that arrives, produces a document and leaves you no better off than before. The point of bringing us in is that your organisation ends up genuinely more secure, and your team ends up knowing more than they did.
- An extension of your team. We work alongside your IT people, in your channels, at your pace. They keep ownership of the estate. We add the depth they do not have on staff.
- In it for the long term. We would rather know your environment for years than audit it once. The second engagement is always better than the first, because we already know how you are built.
- You end up more capable. Every finding carries the reasoning, not just the fix. If your team can close it themselves next time, that is a good outcome, not lost revenue.
- Straight talk. Fixed scope and no surprise invoices. We will tell you when something is not worth doing, and when you do not need us at all.
Our method
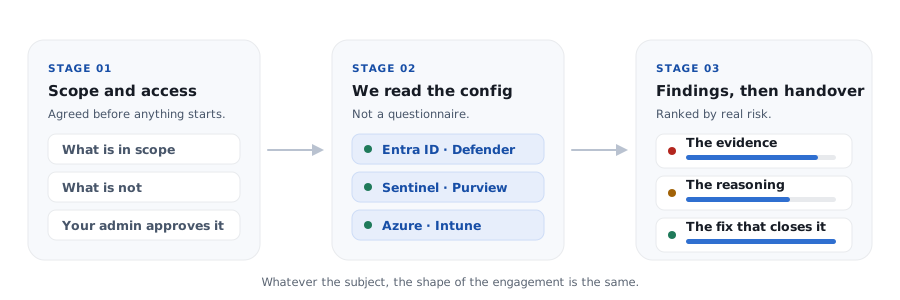
We look at what is configured, not at what someone remembers.
Most security reviews are built on interviews and self-assessment questionnaires. That measures what your team can recall on the day, which is not the same as what your tenant is actually doing. We read the configuration directly and work from that.
- Nothing is self-reported. What we tell you about a control comes from the configuration we read in your tenant, not from an answer on a call.
- Read-only unless you ask otherwise. Assessment access cannot change anything. When we move on to doing the work, that access is separate, scoped to the job, and approved by you on its own terms.
- You can see exactly what we can see. We check every permission before we start, so the access you grant holds no surprises in either direction.
Independent assurance
Already paying someone to run your security?
Outsourcing security does not tell you whether the work is being done, and the reporting you receive comes from the same provider doing the configuring. We read your tenant independently and show you what is actually in place. We are a consultancy, not a managed service, so the review does not arrive with a proposal to take the contract over.
Tell us what you are dealing with.
A short conversation is usually enough for us to say whether we can help, what it would take, and roughly what it would cost. If the answer is that you do not need us, we will say so.